
Changelogs

Follow new updates and improvements to TSplus Insights.

Remote Support is not affected by nginx HTTP/2 vulnerabilities (CVE-2026-123007 / CVE-2026-123633)
Dear Customer,

On November 18, 2026, F5 disclosed two critical vulnerabilities in nginx’s HTTP/2 handling (CVE-2026-123007 and CVE-2026-123633, CVSS 9.2). An attacker could use them to run code on an exposed nginx server without logging in.

TSplus Remote Support is not affected.

Why TSplus Remote Support is not affected

Our Remote Support servers only accept HTTP/1.1 connections. HTTP/2 is not enabled, so these flaws cannot be used against our service. You do not need to do anything for TSplus Remote Support. We will also install the nginx update as soon as Ubuntu releases it.

If you run nginx yourself

For example, as a reverse proxy in front of TSplus Remote Access:

  1. Upgrade to nginx 1.30.7 or 1.31.9, or install your Linux distribution’s update when it is available.

  2. Until then, turn off HTTP/2:

    • nginx 1.25.1 and later: add http2 off; to your server blocks.

    • Older versions (including Ubuntu 24.04’s default 1.24): remove http2 from your listen lines.

  3. Reload nginx and check that HTTP/2 is no longer offered. For example, run curl -sI --http2 https://your-server | head -1 (replace your-server with your server’s address). The answer must start with HTTP/1.1, not HTTP/2.

If you have any questions, please contact our Support team.

Best regards,

Thomas Montalcino
CTO, TSplus

Update - November 20, 2026
We have checked our online websites and services. All instances that were vulnerable have now been patched.
Remote Access - Java4Shell (CVE-2026-114938): how to protect your server

A critical Java vulnerability, CVE-2026-114938 (“Java4Shell”), was disclosed on November 17, 2026. TSplus Remote Access may be affected, because its HTML5 web server runs on the Java 17 runtime (Eclipse Temurin) installed by our setup. We are not aware of any attack against TSplus.

TSplus Remote Support, TSplus Advanced Security and TSplus Server Monitoring are not affected.

Is my server affected? Only if all of these are true:

  • The server runs Java 17.0.6 or newer. The Java runtime installed with TSplus is in this range.

  • The server CPU supports AVX-512 VBMI: Intel Xeon Ice Lake, Sapphire Rapids, Emerald Rapids or Granite Rapids, or AMD EPYC/Ryzen Zen 4 or newer. Older CPUs are not affected.

  • The attacker builds an exploit for one specific application. This is complex: it is sensitive to network conditions and often needs several attempts.

Mitigation (2 minutes)

  1. Open C:\Program Files (x86)\TSplus\Clients\webserver\runwebserver.ini. This is the default path; adapt it if you installed TSplus elsewhere.

  2. Add -XX:-UseBASE64Intrinsics at the end of the first line.

  3. Restart the TSplus web server.

This turns off only the vulnerable Java feature, with no noticeable impact on TSplus Remote Access performance.
Alternative: -XX:UseAVX=2 disables AVX-512 completely, with a wider impact. Use only one of the two options.

Note: if your server runs TSplus 17.20.9.2 or older, check this setting again after each update.

Permanent fix

A TSplus Remote Access update automatically installs the latest Java 17 runtime. It will include the fix as soon as Eclipse Temurin publishes it. This requires access to api.adoptium.net, and the fix is active only after a reboot or a web server restart. Servers without internet access need a manual Java update. We will publish a new entry when the fixed version is available.

If you have any questions or face an issue, please contact our Support team.

Thank you for keeping your servers secure!

Thomas Montalcino

CTO @ TSplus

Remote Support – Direct connection now works behind more routers

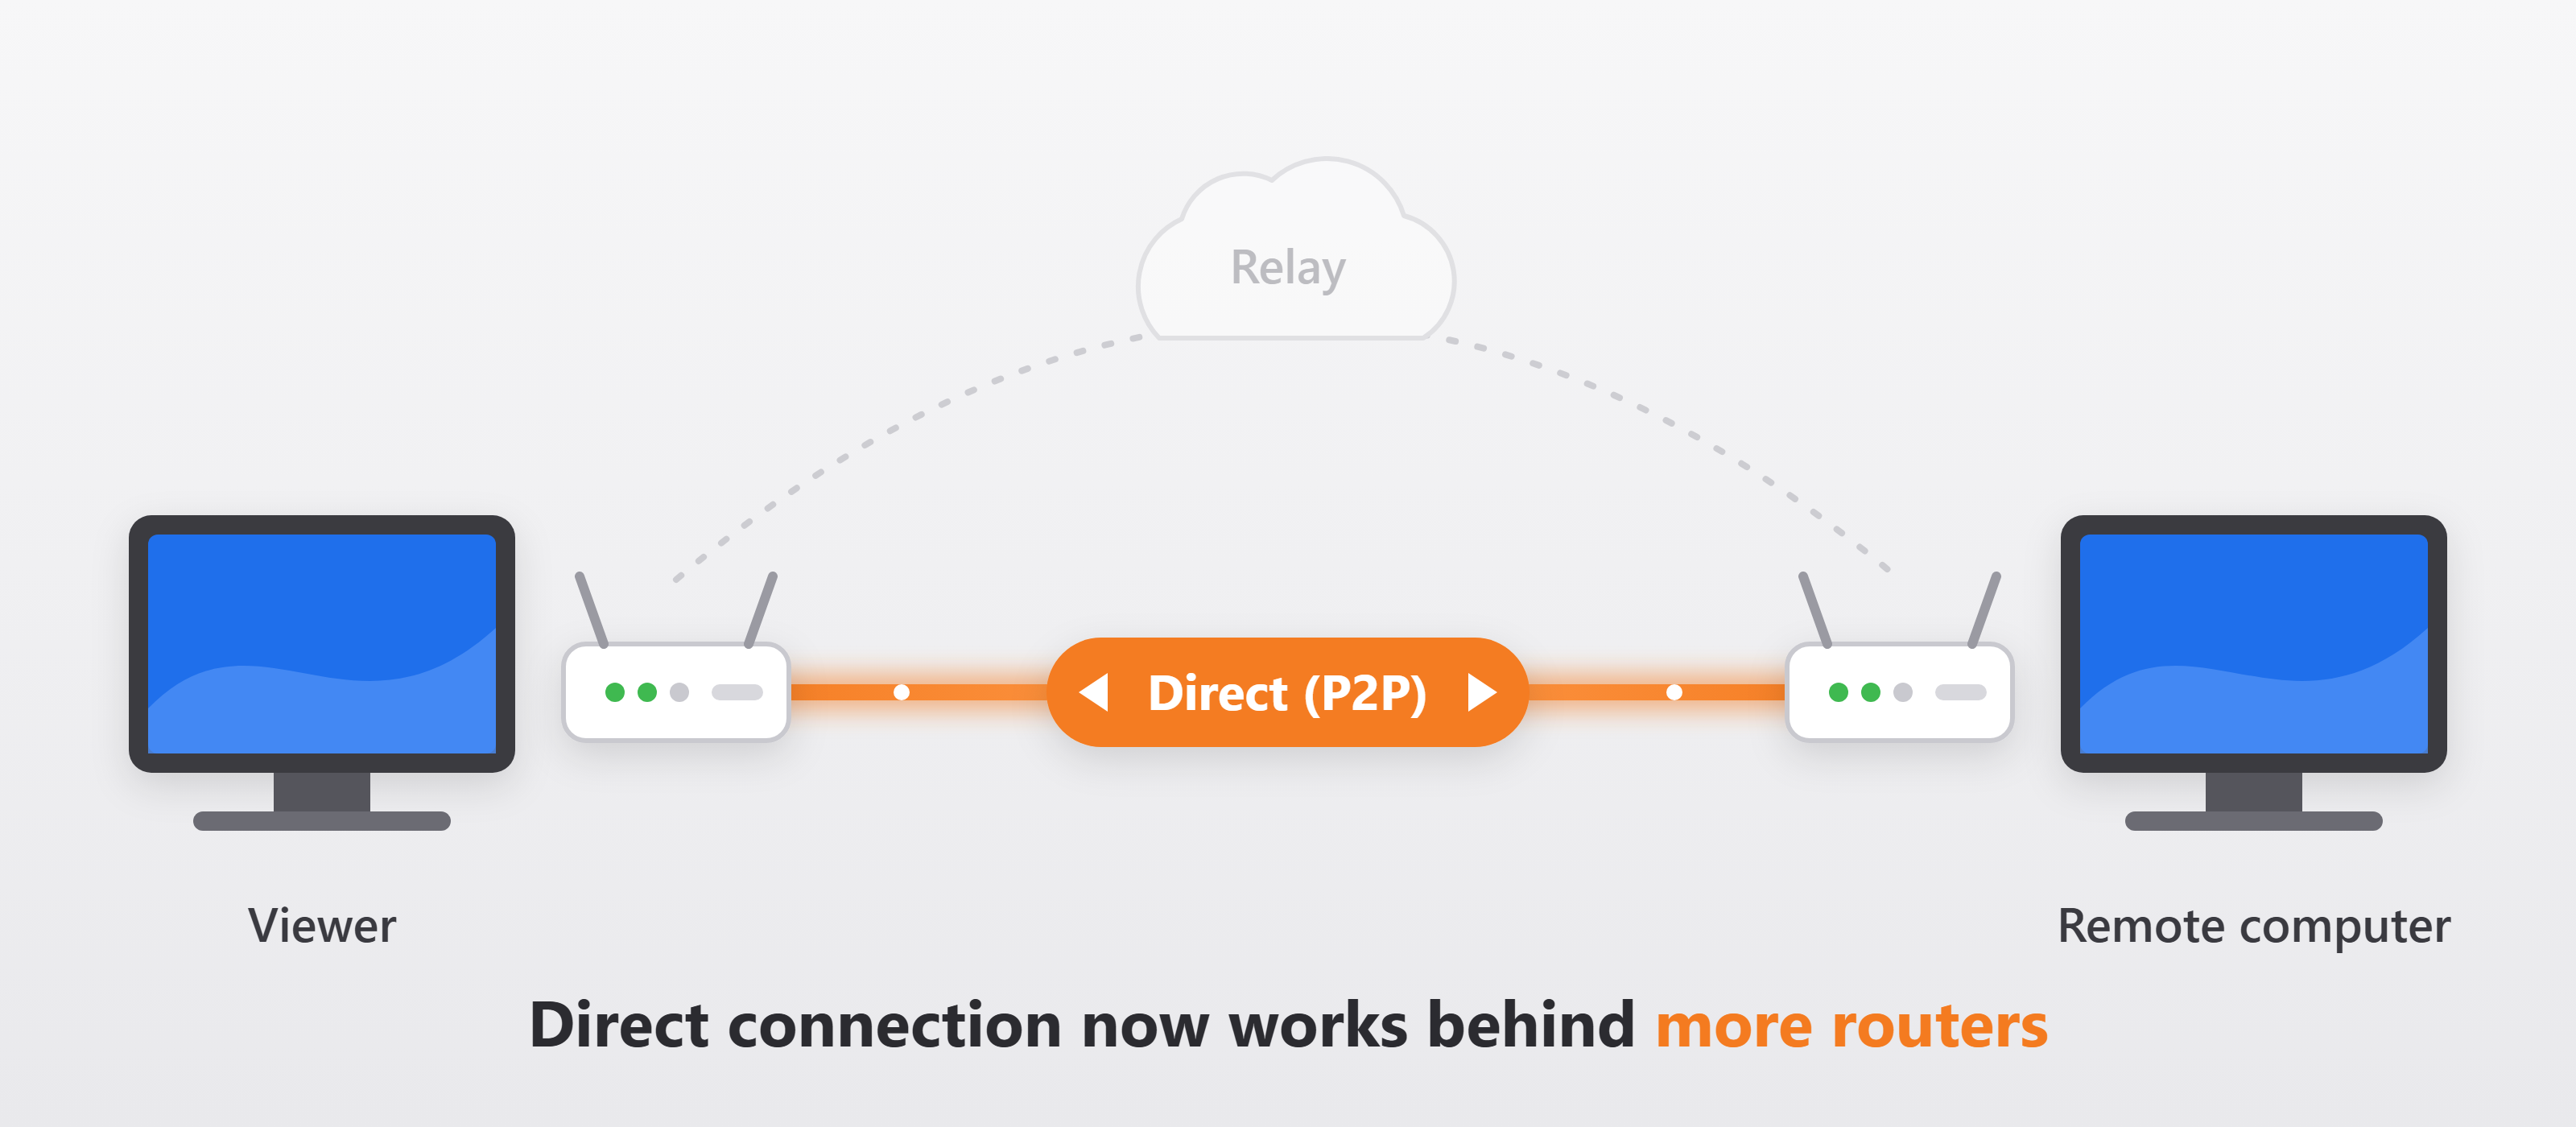
New Remote Support client is out! Direct connection now works behind more routers, so more of your sessions run peer-to-peer for a faster, smoother remote control experience. Windows sessions also stay more responsive when the selected video quality is higher than your bandwidth allows, and the web administration Computers page now keeps online statuses up to date. Full changelog below.

Improvements:

  • Direct connection now works behind more routers

  • Windows: improved responsiveness when the video quality used does not match the available bandwidth

  • Web administration: the Computers page now refreshes the online status of computers automatically every 30 seconds, and a Refresh button allows refreshing it on demand

Fixes:

  • Windows: fixed the viewer sometimes giving up the direct connection right after it was established

Have an idea or issue? To ensure your feedback is properly tracked and addressed, please use our dedicated channels: Support for issues and Feedback for feature requests. Thank you for helping us improve!

Earlier updates